

Free XSS Scanner
Run an online XSS test on your web application and find out if attackers can inject malicious scripts into your pages. Penti's AI pentester launches instantly, hunts for reflected cross site scripting on your live site, and shows you real proof. No setup, no hoops.



What is Cross-Site Scripting (XSS)?
- Reflected XSS: the payload travels inside the request (a URL or form field) and is echoed straight back in the response. Penti's free test targets this class.
- Stored XSS: the payload is saved on the server and served to every visitor of the affected page.
- DOM-based XSS: the injection happens in client-side JavaScript that writes user input into the page.
XSS scanner vs XSS penetration test
There are two ways to look for cross-site scripting, and they do not answer the same question. NIST SP 800-115 draws the line in a single sentence: "While vulnerability scanners check only for the possible existence of a vulnerability, the attack phase of a penetration test exploits the vulnerability to confirm its existence." Penti's free XSS testing is the second kind.
| XSS vulnerability scanning | Penti's free XSS testing | |
|---|---|---|
| What it establishes | That a vulnerability may exist | That it exists, because the AI pentester exploited it |
| How it decides | Responses are compared against signatures of known vulnerabilities, and matches are reported | The agent sends live payloads through forms and URL parameters and checks the response for reflection |
| False positives | Signature-based tools typically carry high false positive rates | Every finding comes with the request and response that prove it |
| Filters and WAF | Encoding and filter bypasses are a known blind spot | The agent retries with encoded payloads and reports the filter or WAF it detects |
| What the report says | Potential risks ranked by CVSS score | Each finding with how it was exploited, the evidence, and a risk level |
| Who interprets it | Results need someone with security expertise to read and rank them | The report explains what was found, what it means, and how to fix it |
What you can do with Penti's free XSS scanner
Penti's free XSS vulnerability scanner runs the OWASP A03:2021 Reflected XSS test, one of two free web application tests on its agentic pentesting platform. Enter your company email and target URL, and an AI pentester probes your site in real time.

Instant XSS test

Security self-assessment

Pre-launch check

Proof for clients and stakeholders

How Penti's XSS scanner works
Launch
Reconnaissance
Discovery
AI testing
Verification
Report
Technical details
The free online XSS scanner tool runs the OWASP A03:2021 Reflected XSS test, rated Medium severity. This XSS website test is AI-powered, runs in an isolated environment, and finishes in a few minutes with nothing to configure.
| Detail | Value |
|---|---|
| Test | OWASP A03 · Reflected XSS |
| Severity | Medium |
| Designed for | Web applications (webapp targets) |
| What you enter | Company email + target URL or hostname (must start with http or https) |
| Engine | AI-powered agentic pentest, runs in an isolated environment |
| Standards | OWASP Top 10 and OWASP Testing Guide, NIST Cybersecurity Framework, MITRE ATT&CK |
| Typical run time | A few minutes |
| Free tier | 1 test at a time; up to 3 tests per month per business address |
XSS scanner results
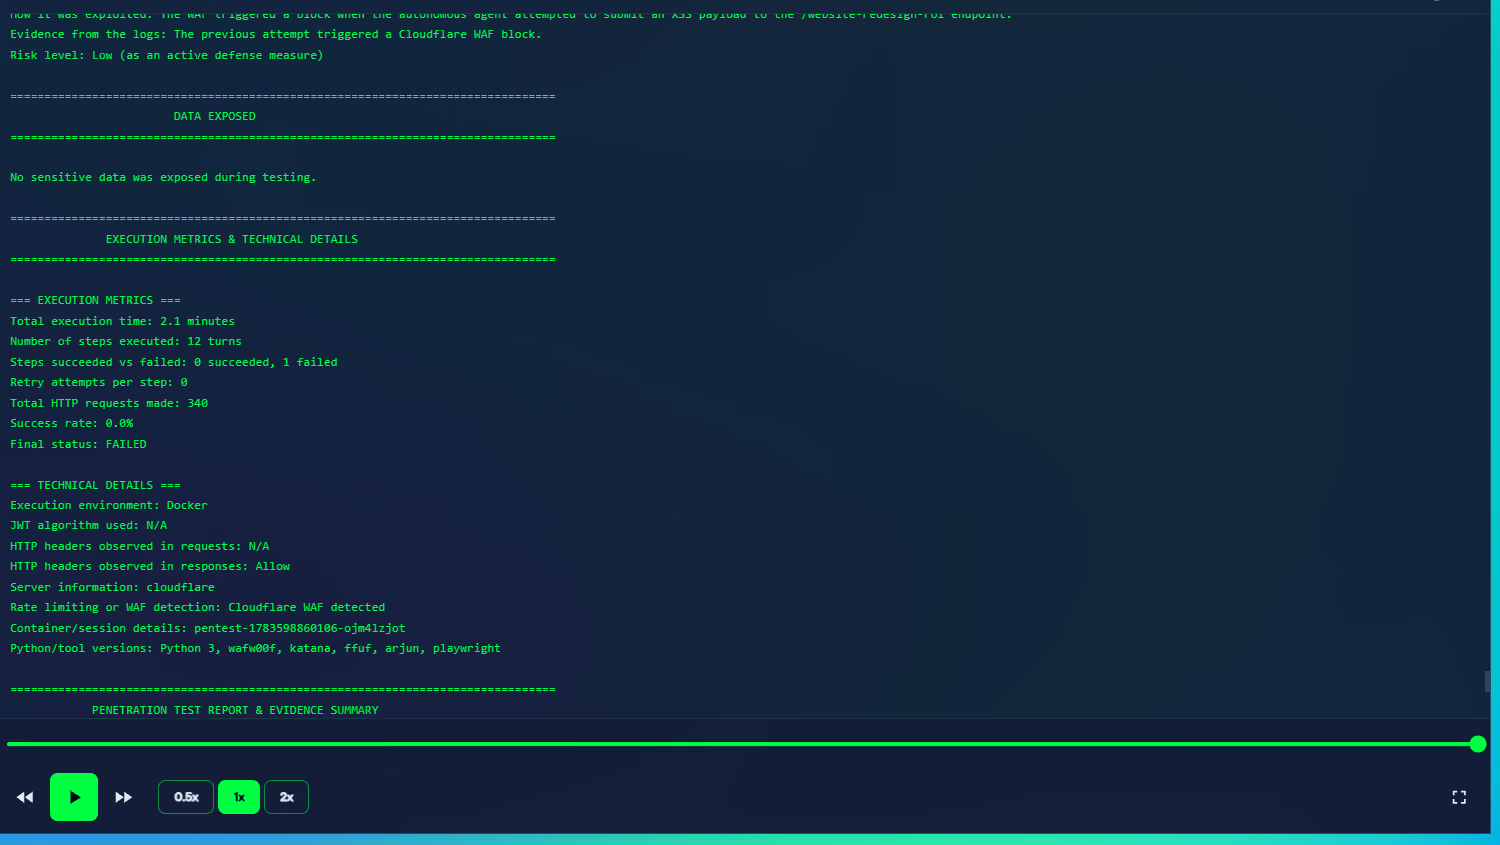
Every test for XSS ends with a full Penetration Test Evidence Log, shown on screen at the end of the live run. It walks through everything the AI pentester did, in this order. The report ends with a clear verdict and a findings count: confirmed cross site scripting vulnerabilities with proof, or a clean result with hardening recommendations.
HTTP Requests and Responses

The full request and response for each tested URL.
Endpoint Enumeration
Every endpoint tested with its status (200 / 403 / 404) and a summary count.
Authentication Details & Vulnerabilities Confirmed
The authentication process that was checked, plus each confirmed vulnerability with its name, description, how it was exploited, evidence from the logs, and risk level.
Data Exposed
Whether any sensitive data was exposed during testing.
Execution Metrics & Technical Details
Total time, steps executed, HTTP requests made, success rate, execution environment, and the detected server or WAF.
Report & Evidence Summary
A Security Assessment of your overall posture and risk, plus an Executive Summary of what was tested, what was found, and how to fix it.

Why use Penti's XSS scanner
Penti gives you a real pentest, not a surface scan: proof-based results that strengthen your web application security, with clear fixes and no setup.
Real exploit detection
Agentic and fast
Proof you can trust
Built-in remediation

Free and instant

Room to grow
How to prevent XSS attacks
Here is how to check for cross site scripting vulnerabilities and prevent them. A few disciplined secure coding practices close the security flaws attackers exploit and reduce XSS and other web vulnerabilities. Penti automates the testing: the free XSS checker re-tests your app on demand and shows exactly where input is reflected.

Validate and escape user input

Use output encoding libraries

Set a Content-Security-Policy

Prefer allowlists over blocklists
Use HttpOnly cookies
Test after every release
What our clients say
For security teams turning to AI to stay ahead of threats and cut costs, Penti delivers real pentest results without the wait.


Penti's service is a game changer for our compliance needs. The insights we gained were invaluable for our team. Doing this well is crucial for our compliance targets and key in advancing our strategic initiatives.

The integration between Penti, our system, and third parties like Vanta is exceptional. I would also like to mention that their response times are extremely fast!

Penti has been like having an experienced and nimble Security Engineer on staff. They have outlined issues in our platform and guided us towards implementations and fixes that allow for us to ensure we are treating our users data with the utmost care.
Other free tools
Hardcoded Secrets
Learn moreWeak JWT Secret
Learn moreGrafana Path Traversal (CVE-2021-43798)
Learn moreOpen Redirect (External)
Learn moreFAQ
What is an XSS vulnerability?
Cross-Site Scripting lets an attacker inject a malicious script into a web page that then runs in another user's browser. It happens when user input is shown on the page without proper validation or escaping.
What is Reflected XSS?
Reflected XSS is the Cross-Site Scripting class where the malicious script travels in the request (a URL or form field) and is echoed straight back in the response, running in the victim's browser. It is the flaw Penti's free test checks for (OWASP A03:2021).
How to test a website for XSS?
Enter your company email and the target URL, then start the free test. Penti's AI pentester crawls your app, injects real reflected-XSS payloads, and shows what it finds on screen, with nothing to install.
Do I need to install anything?
No install, nothing to configure. Just enter your company email and target URL to start the XSS tool.
Do I need permission to scan a site?
Yes. Only test a target you own or are authorized to assess. You confirm this by accepting the Terms of Service and Pentesting Agreement before the test starts.
Are there any limits?
The free tier runs one test at a time, up to three tests per month per business address. Starting a test only needs your company email, no account setup.
What do I get at the end?
A full evidence report: an executive summary, confirmed findings with evidence, and recommendations for remediation.
How to fix an XSS vulnerability?
Follow the report's remediation recommendations, apply the prevention tips above, then re-test.